
Este es el que agregas al carrito
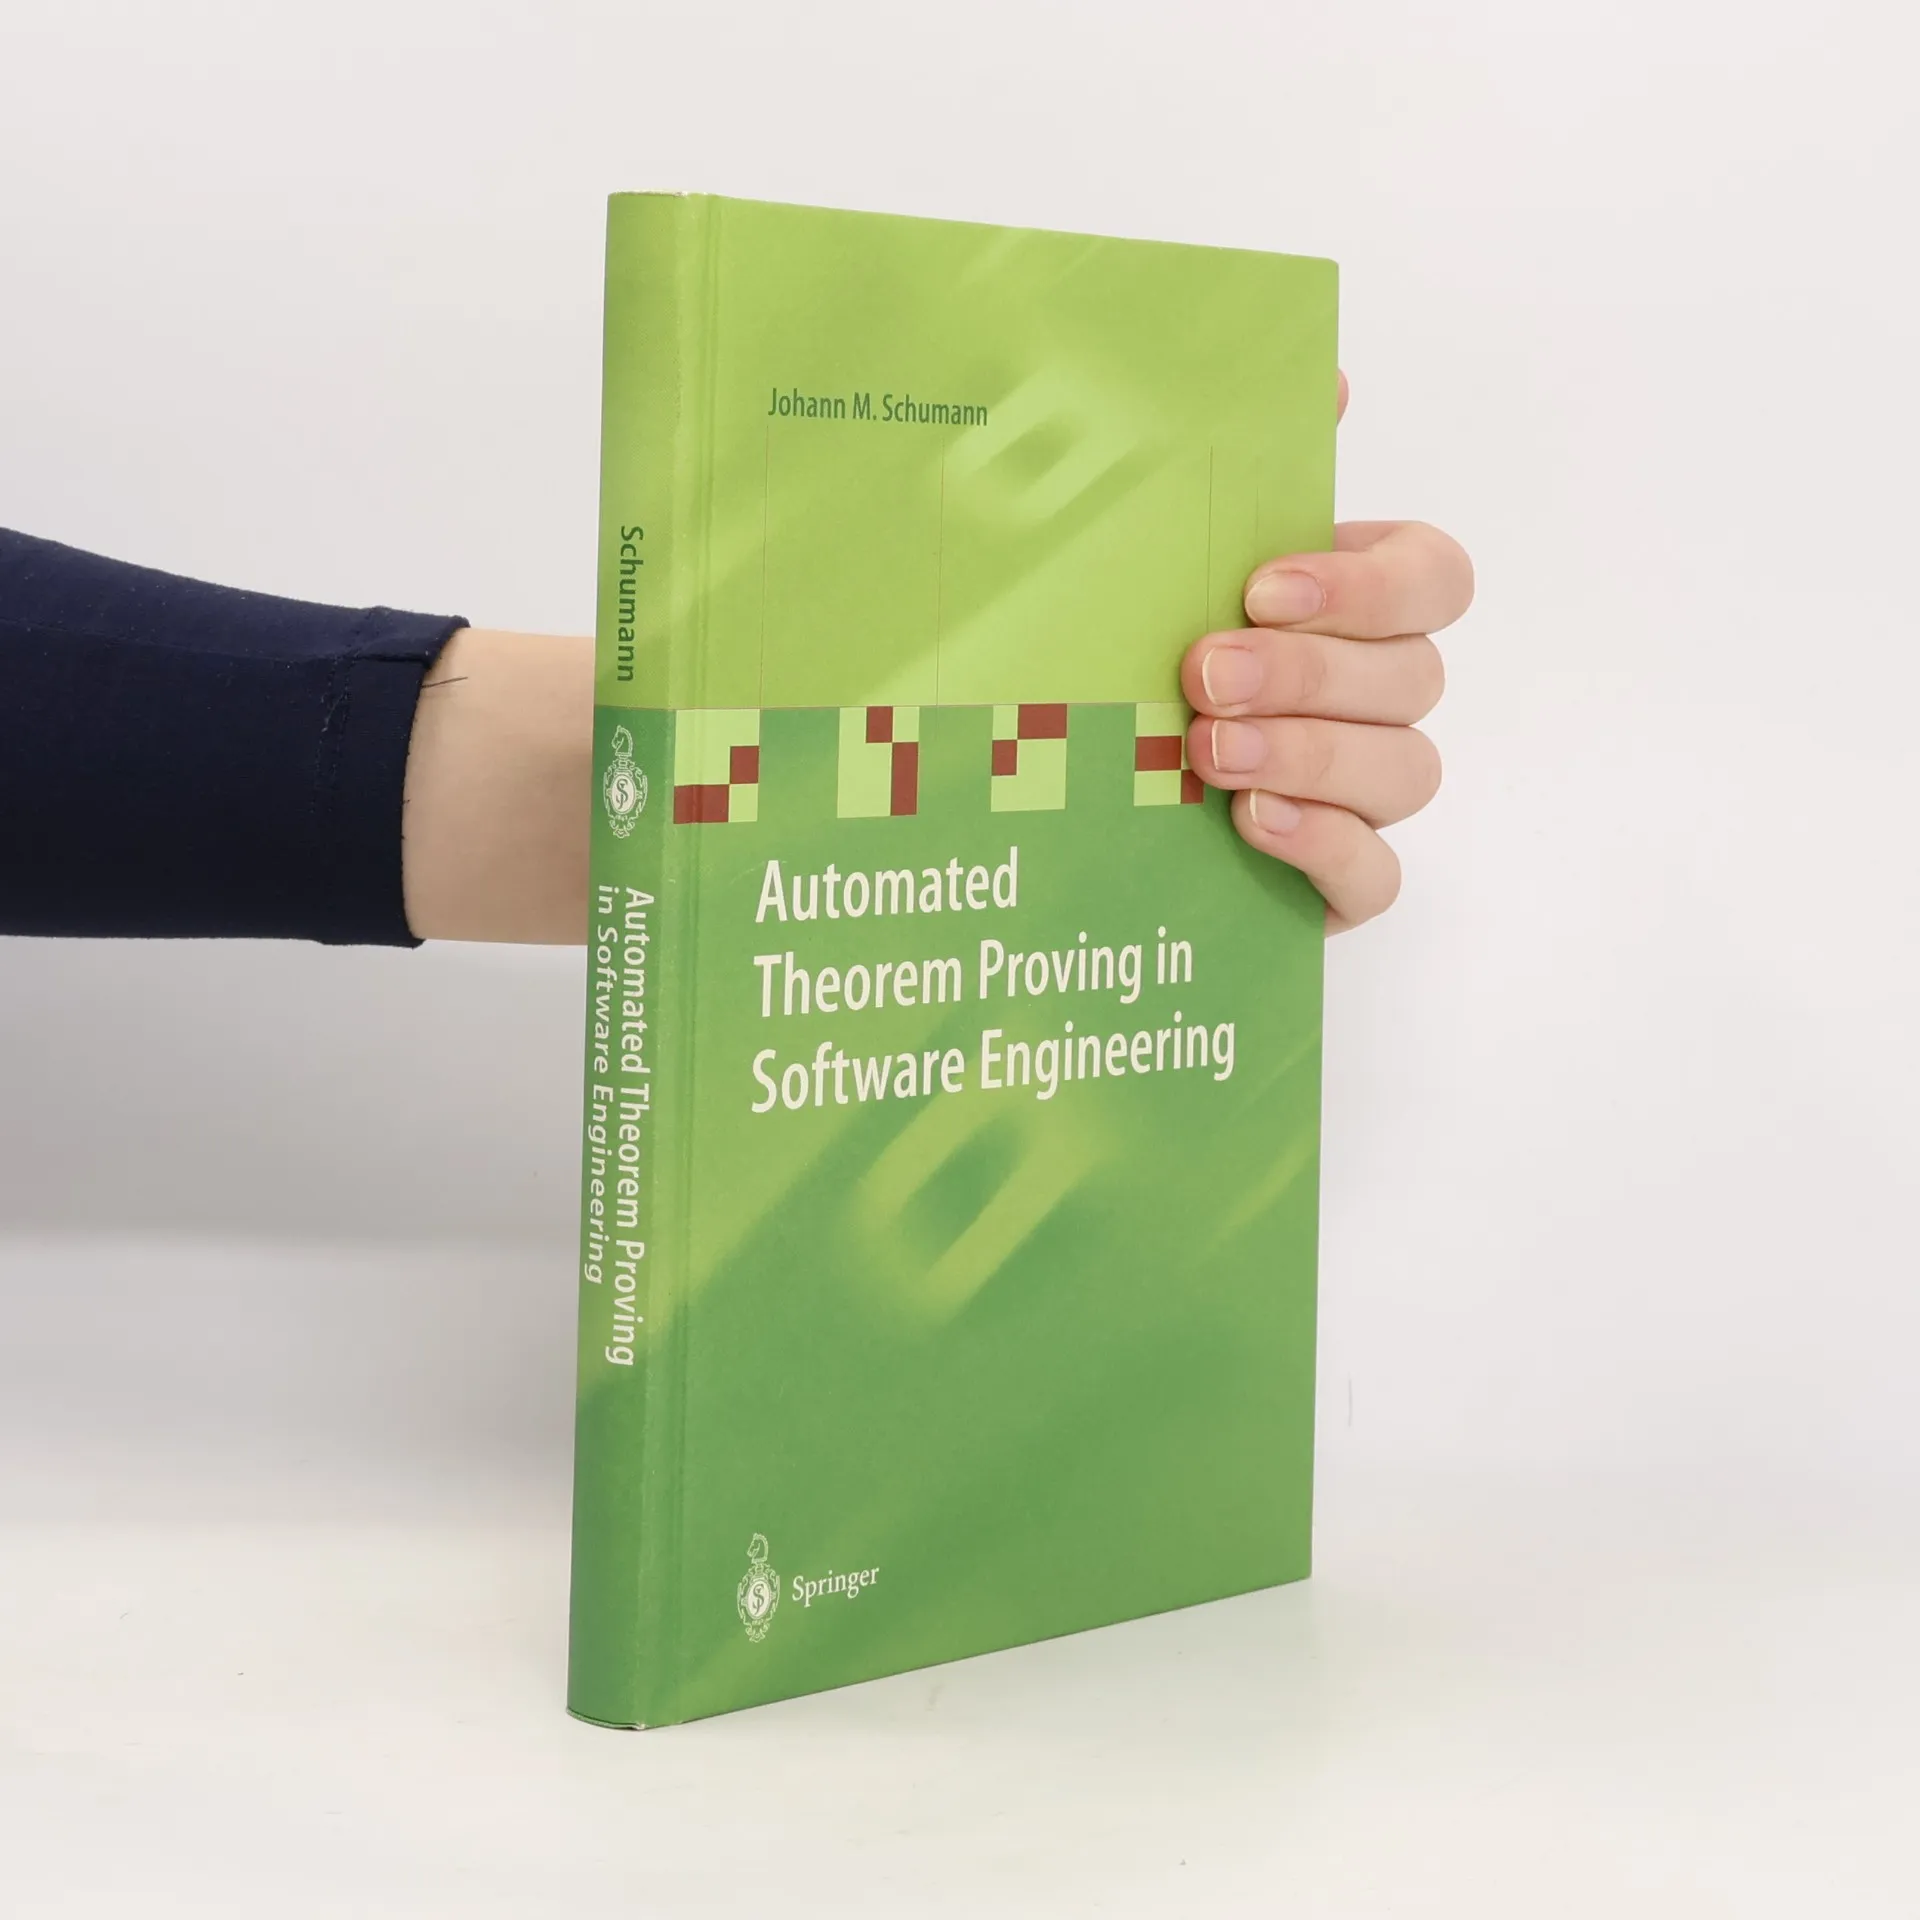
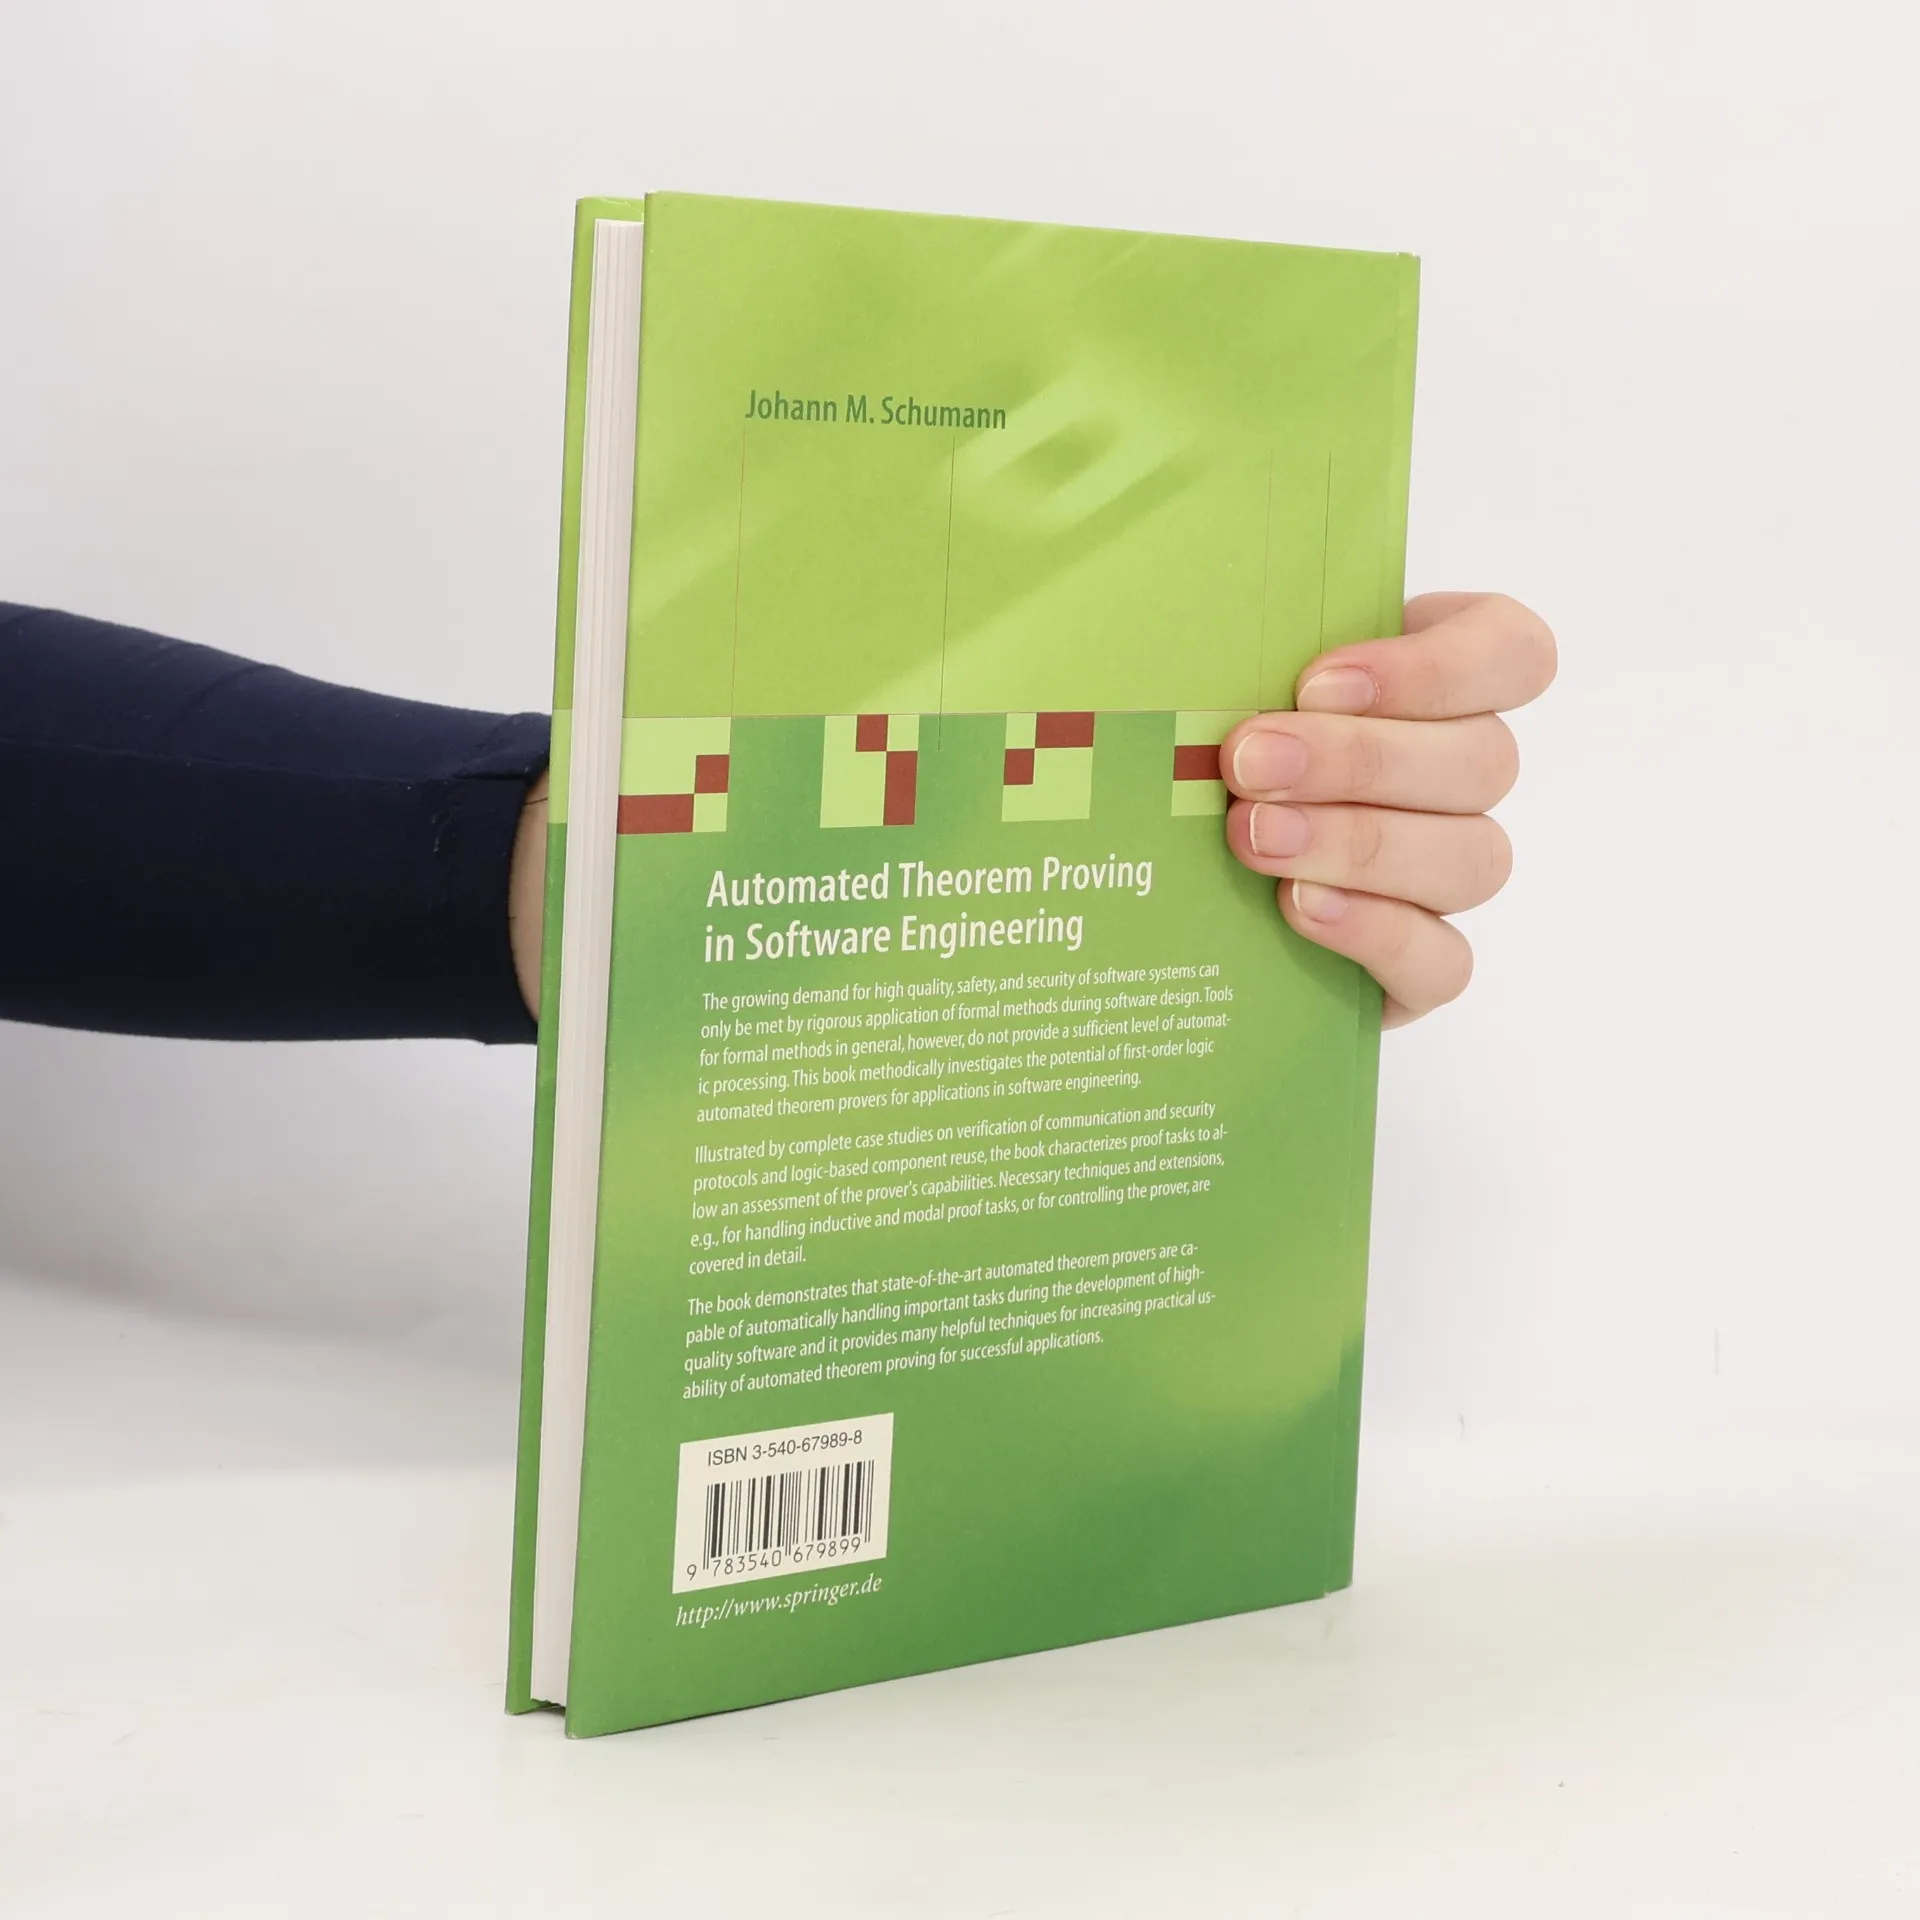
Automated Theorem Proving in Software Engineering
Parámetros
- 228 páginas
- 8 horas de lectura
Más información sobre el libro
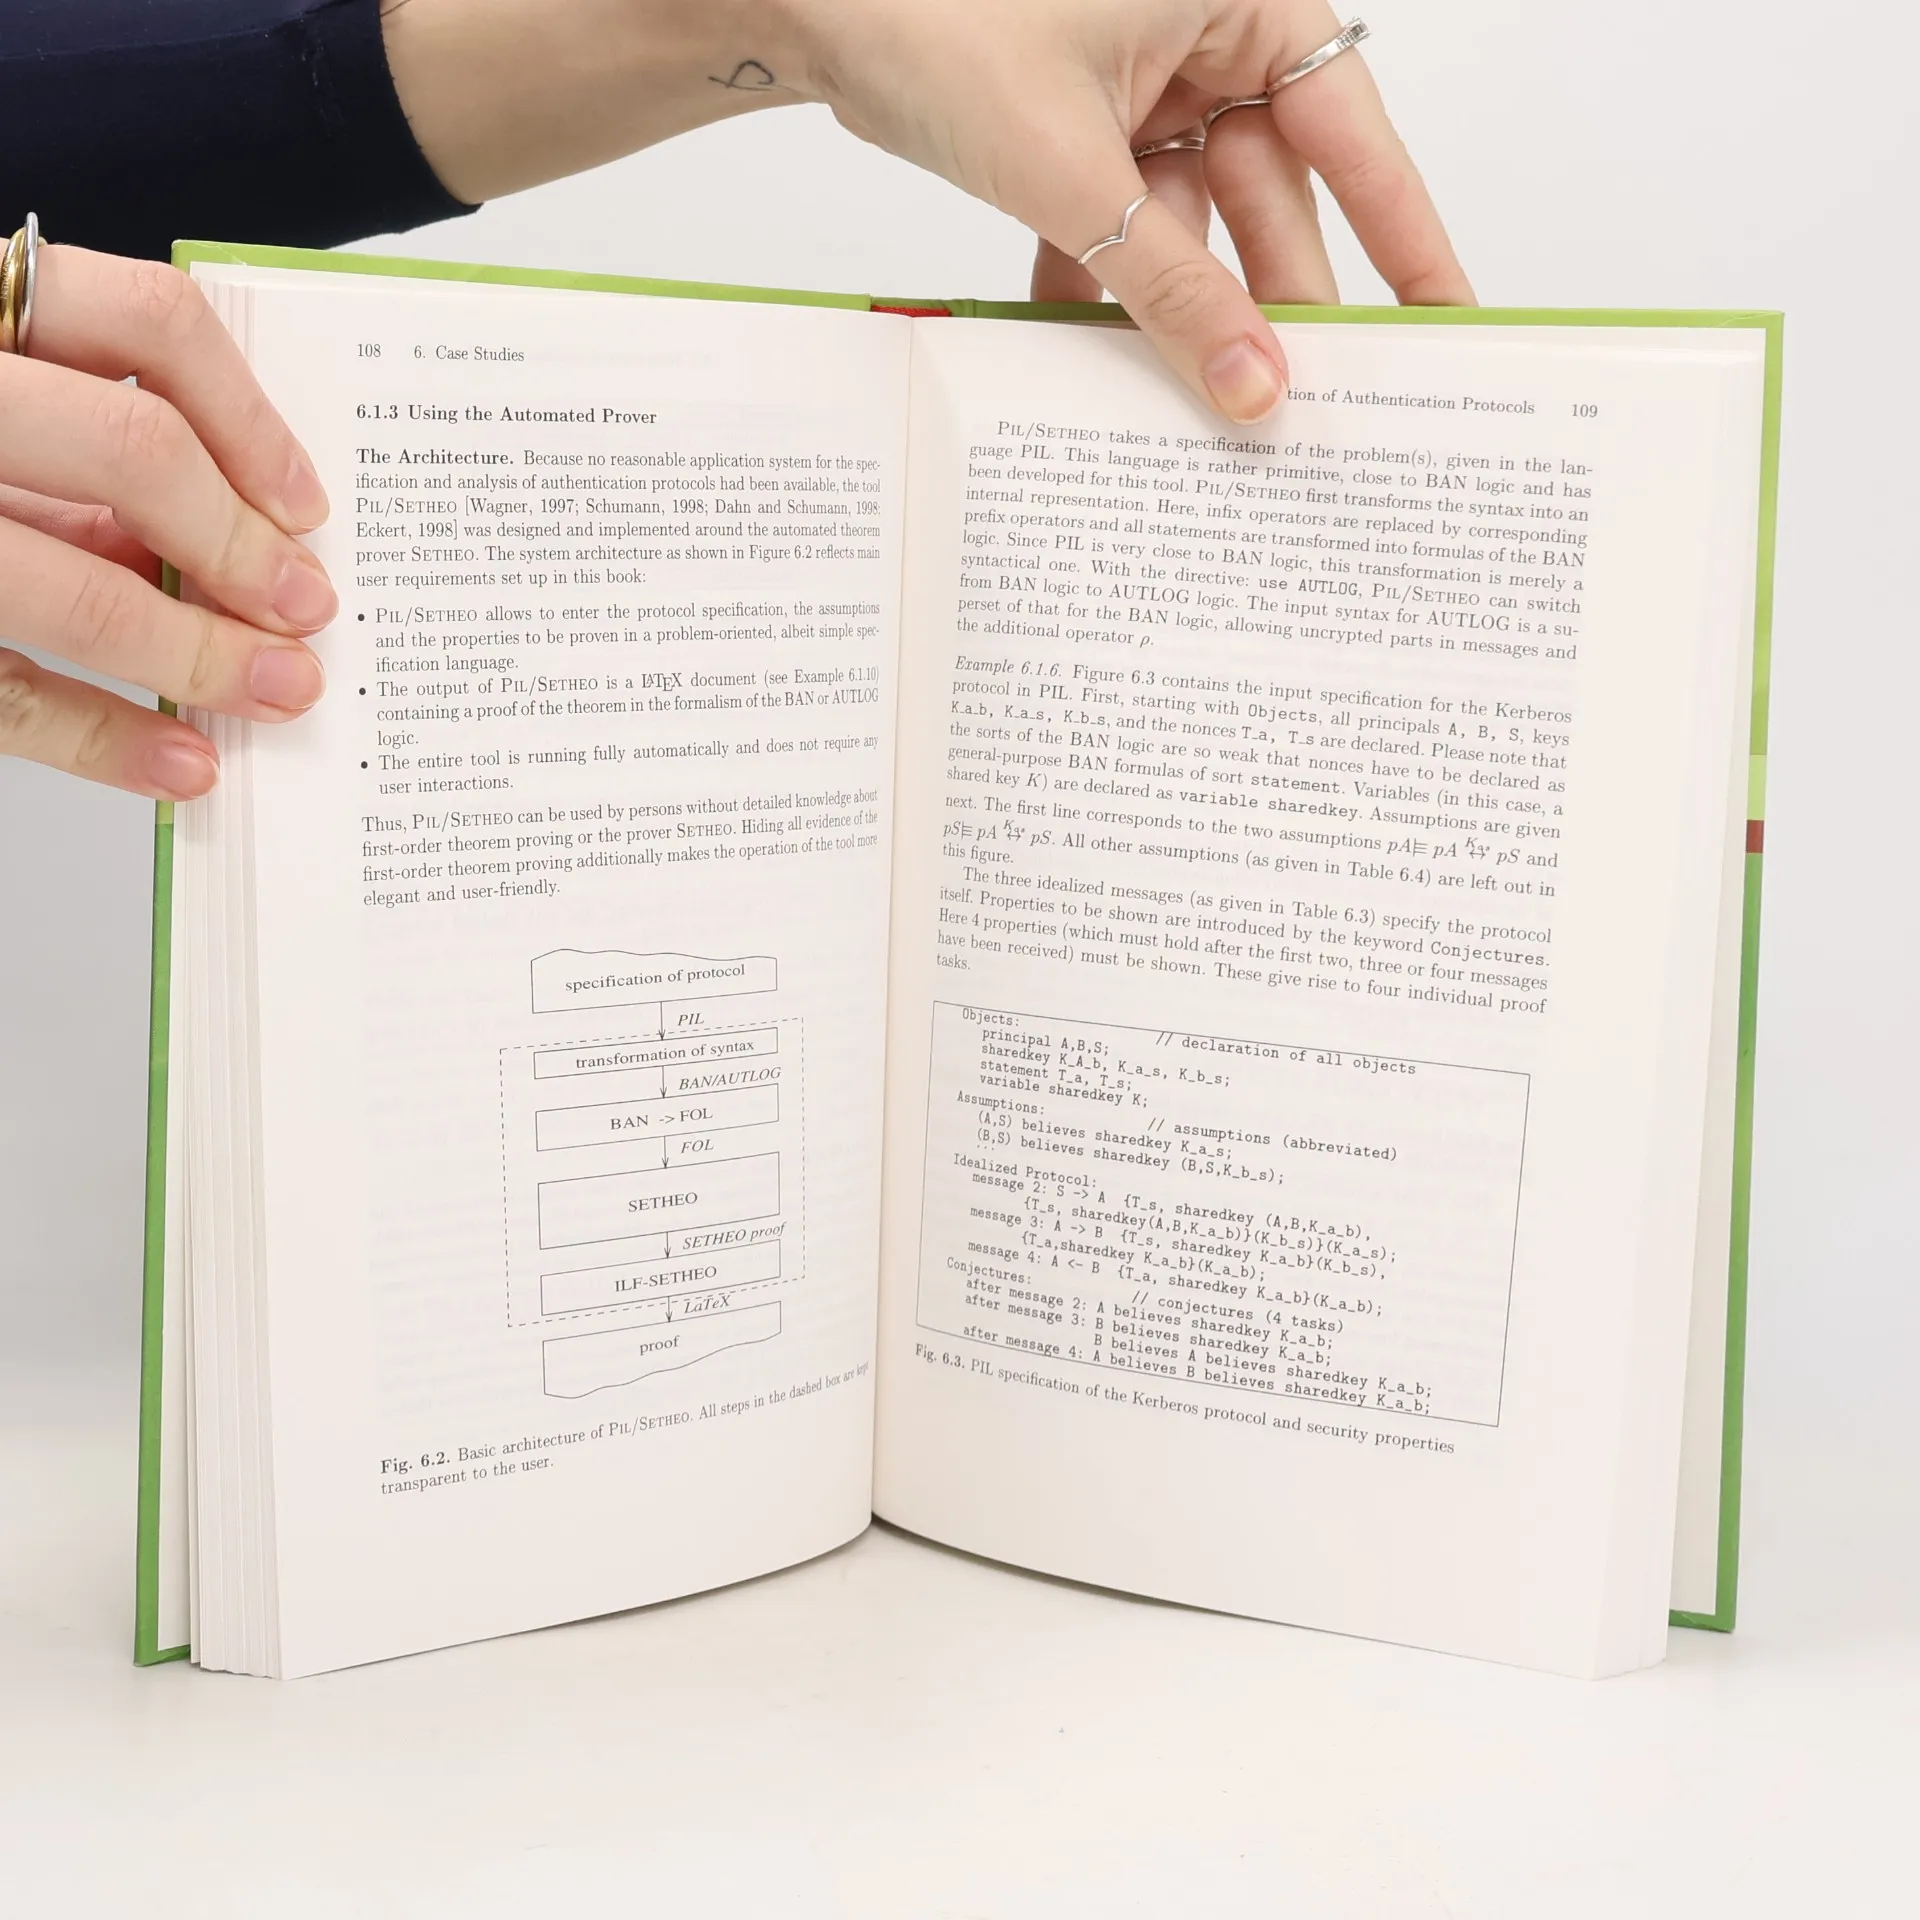
Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.
Compra de libros
Automated Theorem Proving in Software Engineering, D. Loveland, Johann M. Ph. Schumann
- Idioma

- Publicado en
- 2001
- Encuadernación
- (Tapa dura),
- Estado del libro
- Bueno
- Precio
- 31,99 €
Métodos de pago
Nadie lo ha calificado todavía.
- Título
- Automated Theorem Proving in Software Engineering
- Idioma
- Inglés
- Autores
- D. Loveland, Johann M. Ph. Schumann
- Editorial
- Springer
- Publicado en
- 2001
- Formato
- Tapa dura
- Páginas
- 228
- ISBN10
- 3540679898
- ISBN13
- 9783540679899
- Serie
- Categorías
- Etiquetas
- Arquitectura, Europa Occidental, Inteligencia Artificial, Lógica, Sistemas operativos, Desarrollo de Software, Sistemas de Información
- Descripción
- Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.